

Dark Web Monitoring API: First Post Filters
A first-post-only query can hide later replies. Follow one constructed thread through retrieval, storage and alerts to find where an update disappears.

Over the past year, the number of cyber attacks has continued to grow, and today, according to the Cisco Annual Cybersecurity Report, attackers can launch campaigns without human intervention.
With the threat landscape always changing, it is always important to constantly monitor for new attack vectors. Our cyber team dived deep and using our Cyber API, we found the most popular attack vectors mentioned on the dark web in 2021:
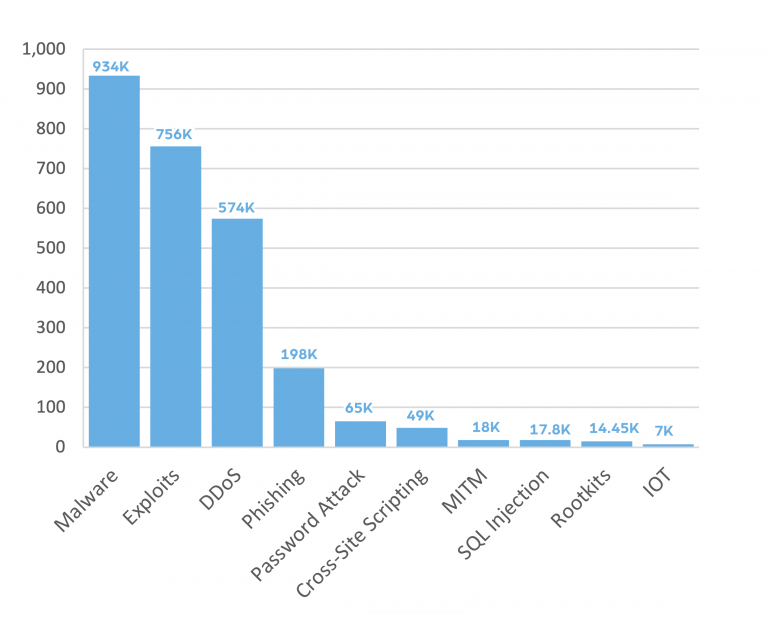
According to our data, the top 3 attack vectors are malwares, exploits and DDoS attacks. We see malware, a malicious code in the form of virus, ransomware, spyware or others, traded in the dark web on a regular basis. In the image below you can see a post we found on Raidforums, in which a threat actor is looking to gain access to a malware:
Malware, exploits and CVEs are basically malicious code that are executed on an organization’s assets such as: servers, PCs, or mobile devices. Any one of them is considered as a high risk to an organization. Cybersecurity, brand protection and threat hunting solutions monitor the dark web to track these indications, assess their level of threat and when needed, take action to protect the organizations they are monitoring.


A first-post-only query can hide later replies. Follow one constructed thread through retrieval, storage and alerts to find where an update disappears.

A vendor breach notice and an exposure search answer different questions. Map both to your service inventory before deciding which accounts need attention.

How a password-required import rule can hide AI token exposure, with a worked example and a test that checks whether the finding reaches an analyst.


