

How to Automate Supply Chain Risk Reports: A Guide for Developers
Do you use Python? If so, this guide will help you automate supply chain risk reports using AI Chat GPT and our News API.

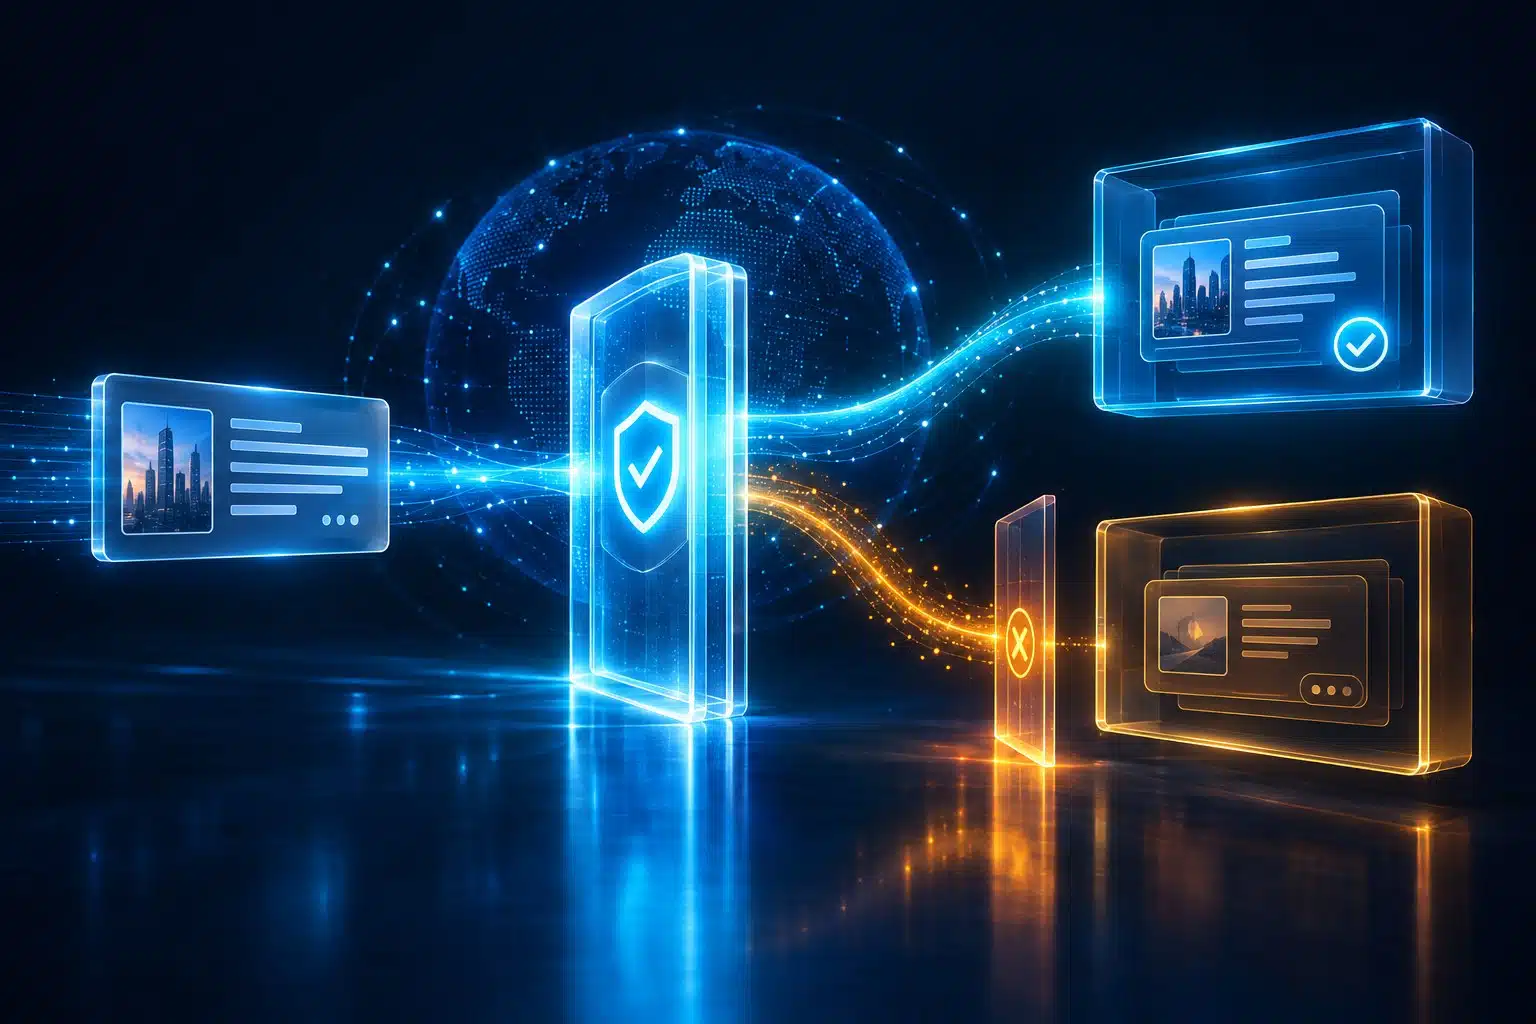
A signed news-monitoring webhook can reach the wrong customer, even if its signature is valid. The receiver may properly authenticate the sender and then trust a workspace identifier that the customer supplied when creating the monitor.
On November 16, 2026, Perplexity launched its Monitor API. It schedules web and news searches and delivers relevant updates via signed webhooks. Its announcement describes metadata for routing updates to users, workspaces, or agents. This raises a practical challenge to developers of news agents for multiple customers: who gets to determine which workspace owns an incoming update?
The best approach is to resolve ownership from the application’s saved monitor record prior to an agent seeing the update. A signed message protects the integrity of the message and authenticates it against the signing secret. However, it does not prove that all the routing instructions were authorized by the application.
In this constructed example, a news-monitoring service that hosts workspaces A and B has an authenticated user in A that creates a supplier news monitor via the service’s setup form. The service creates the external monitor with its integration credentials, but captures a workspace field from the form in the monitor’s metadata.
The user submits B instead of A in the workspace field. Later, a legitimate, signed update with that metadata arrives to the receiver. The update is processed and A’s monitor output is sent to B.
No forged signature is needed. The problem occurred when the application allowed customers to determine ownership. Webhook delivery only advanced the error. Even if the news article is publicly available, the watchlist association may reveal what a customer is researching. A downstream agent could also put the evidence in the wrong customer’s case.
OWASP’s description of broken object-level authorization explains that just receiving a valid object ID is not adequate; the application also needs to evaluate permissions for the object and the action requested. In this context, verifying the provider is just one check. Authorizing the monitor’s destination is the other.
When a monitor is created, make sure the user who created it is allowed to create monitors in that tenant. Derive the workspace owner from the authenticated session and store the provider returned monitor ID against that owner, along with the approved destination. Customer supplied metadata can be beneficial, but it must not be used to override this data.
A practical receiver design uses an opaque endpoint handle to look up the expected monitor and the signing secret. The handle is an aid in looking up the monitor, not an authentication token. It avoids picking a tenant’s key because an unverified body names that tenant.
Per Perplexity’s documentation of Standard Webhooks v1 verification, verify the signature over the original request bytes, and signed header values. Enforce a timestamp tolerance of five minutes against your clock before processing. Perplexity’s events include a monitor snapshot. After verification, compare the monitor ID of the event to the record selected by the endpoint handle.
For A’s update, keep the saved owner as A. Treat a mismatch in signed metadata as a quarantined violation rather than as a new routing instruction. A mysterious monitor should not result in automatic workspace creation or a default fallback to a different customer.
Save the resolved route with the accepted event, and do not allow a worker to recalculate the destination from the original metadata. If the customer changes the destination, require an authorized settings change and define whether previously queued events should follow the old route or the new one.
When the agent obtains additional coverage, the same ownership rule applies. Webz.io’s News API provides structured articles, and the documented post fields of the API include a UUID, URL, extracted text and publication time. The customer can choose to retain those fields so the analyst can access the evidence.
For this example, combine the article and the agent’s assessment with A’s case. Public source text does not grant access to A’s case notes, case analyses, or access to A’s watchlist. Restricted tenant controls must also cover stored research and any later retrievals by the agent.
An unverified allegation may be contained in a properly routed report. Preserve attribution when the article reports an allegation, and let the review policy decide whether the finding warrants action. Correct routing and sound evidence assessment address different concerns.
Use a receiver fixture with A’s registered monitor and an approved destination in A. Sign a test event with the configured test secret, but set the metadata workspace to B. The signature check should pass, and the routing check should hold a mismatch. Check the destination records to see if B received anything.
Submit an event with A’s expected monitor ID and consistent metadata. It should put the event in A’s queue, and be processed with its source context. Also test a correctly signed event naming an unregistered monitor: it should not acquire an owner just because the signature passed.
Alert retries need their own delivery checks, according to Webz.io’s guide to retrying news-monitoring jobs. Here, an actual incoming update should never choose its customer by itself.


Do you use Python? If so, this guide will help you automate supply chain risk reports using AI Chat GPT and our News API.
Use this guide to learn how to easily automate supply chain risk reports with Chat GPT and news data.
A quick guide for developers to automate mergers and acquisitions reports with Python and AI. Learn to fetch data, analyze content, and generate reports automatically.


